
That means you gain all the advantages of having wealthy visibility over your cryptographic keys with out confining them to a single repository. As An Alternative of putting all your eggs in one basket, your property are distributed in accordance with your needs. Keyfactor provides security teams visibilityand control over the identities and cryptography that secure every digital interplay, so your business keeps running—uninterrupted. Posture administration offers a unified view of what cryptographic property exist, where they’re deployed, and the way they’re configured. Cryptographic posture is essential to find a way to know what’s under the hood, but additionally to be properly prepared. Key usage and metadata, together with creation, validity and expiration dates, have to be documented for regulatory compliance, covering frameworks similar to NIST SP , PCI DSS, HIPAA, and GDPR as applicable.
Key Types And Operations In Key Management Service
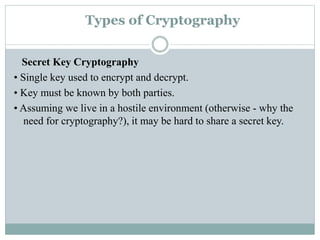
Options like BYOK enable organizations to retain management over their encryption keys even when utilizing third-party cloud services. These instruments often combine with key management techniques to automate the handling of secrets, guaranteeing sensitive knowledge is encrypted and guarded with strict access controls. For many organizations, encryption is probably one of the best measures to secure sensitive data. It applies the principles of cryptography to remodel readable knowledge into ciphertext through the use of cryptographic algorithms, making it inaccessible to unauthorized customers. Public/private key pairs are used for a safer methodology of encryption referred to as asymmetric encryption.
Encryption protects the data within the cloud, and to ensure its confidentiality and integrity, securing the encryption keys is of paramount importance. A key management system can help automate and implement key insurance policies, making the process even more efficient and reducing errors. It may help organizations strengthen information safety, forestall unauthorized access and comply with regulatory standards. In an era the place digital communication underpins almost every facet of our lives, the importance of securing sensitive data can’t be overstated. Cryptographic keys serve as the backbone of contemporary encryption methods, enabling secure information transmission, authentication, and privacy in a world increasingly weak to cyber threats. Whether Or Not you are a cybersecurity skilled, a software program developer, or a business leader, understanding cryptographic keys is crucial for safeguarding your digital belongings.
Reminiscence Management Considerations In Encryption Key Administration
- Symmetric algorithms are the commonest kind of encryption algorithm.
- The key rotation course of entails decrypting knowledge with an old encryption key, then re-encrypting the data with a new encryption key.
- Some options, similar to a key management service (KMS) and open-source key administration instruments, supply flexible and customizable options.
- Symmetric-key algorithms (sometimes often identified as secret-key algorithms) remodel information in a method that is essentially tough to undo without data of a secret key.
IBM offers comprehensive data security services to guard enterprise information, purposes and AI. KMIP is not a key management solution however a standardized protocol designed to facilitate the interoperability of key management methods across totally different platforms and suppliers. Storing keys in software may be extra handy, however it may possibly additionally carry the next security threat than hardware-based storage solutions like HSMs. Discover various views on cryptography with structured content material masking algorithms, functions, vulnerabilities, and future developments in safe information methods.
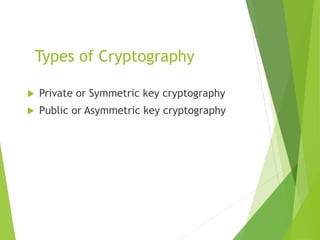
Making Certain that keys are random and unpredictable helps mitigate weaknesses that can compromise the entire encryption process. For each encryption strategies, proper key management is important for safeguarding information and sustaining the integrity of encryption systems. Each the sender and the receiver share a secret key that permits them to encrypt and decrypt messages. This methodology https://homadeas.com/voice-tag-lab-the-best-solution-for-recording-audio-files.html works shortly because it uses a single key for both processes. Nevertheless, the problem lies in securely sharing that key with out it being intercepted. Encryption, aka cryptography, is used to safe knowledge at rest, stored in servers, and in motion, as transmitted over the network.
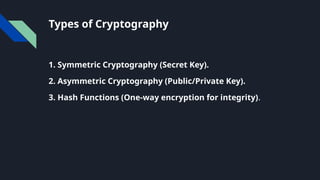
Key administration, or management of encryption keys, is the process of putting sure requirements in place to make sure the safety of cryptographic keys in a company. Mainly, it is the separation of keys from information to realize flexibility and security. Encryption is a cryptographic operation that converts plaintext into ciphertext, thereby securing delicate information and rendering it unreadable. The encrypted information can solely be made readable once more if the entity attempting to access the knowledge has the requisite cryptographic keys to decode the ciphertext. Encryption is a way for data—messages or files—to be made unreadable, ensuring that only an authorized individual can entry that information.
Asymmetric-key Algorithms
This follows the precept of securing knowledge at rest and is helpful for reconstructing a key from archived keying information. FIPS186 specifies algorithms that are approved for the computation of digital signatures. Message Authentication Codes (MACs) present data authentication and integrity. A MAC is a cryptographic checksum on the info that’s used in order to present assurance that the info has not changed and that the MAC was computed by the anticipated entity.
Cryptography is the science of protecting data using mathematical techniques to make sure confidentiality, integrity, and authentication. It transforms readable knowledge into unreadable kind, preventing unauthorized entry and tampering. Shield knowledge everywhere—enforce robust encryption, handle keys and secure delicate data across on-premises and cloud environments. CloudHSM services can extend these capabilities to the cloud, providing the same stage of safety for cloud-based environments. Organizations that need to fulfill strict compliance necessities, similar to PCI DSS or GDPR, would possibly select HSM, knowing that keys never depart the secure environment.
Implementing cryptography in Node.js is simple, and with safe key management practices, you can ensure your purposes are protected. Key management companies are cloud-based solutions provided by third-party providers. These services handle the lifecycle of cryptographic keys, including generation, storage, rotation and destruction.
Organizations must typically manage hundreds of encryption keys across completely different methods and environments, each at various levels of their lifecycle. Today, organizations increasingly prioritize encryption and key management to strengthen their cybersecurity. According to the Price of a Data Breach report, organizations that use encryption can reduce the monetary influence of an information breach by over USD 200,000. Non-public keys enable customers to access their funds, whereas public keys permit others to ship transactions securely. Banks use cryptographic keys to encrypt customer data throughout online transactions.


